Worked example
Ardel TCU-40
A fictional telematics control unit, used to show what a completed set of supplier work products looks like.
Ardel and the Ardel TCU-40 telematics control unit are fictional.
Free 4-page Ardel overview (PDF)
Follow the fictional Ardel TCU-40 from the first supplier questionnaire to release and field vulnerability handling. The PDF is in English.
Inside the Ardel example
Two excerpts from the English overview show how the kit connects responsibilities to engineering evidence.
Who owns each activity? 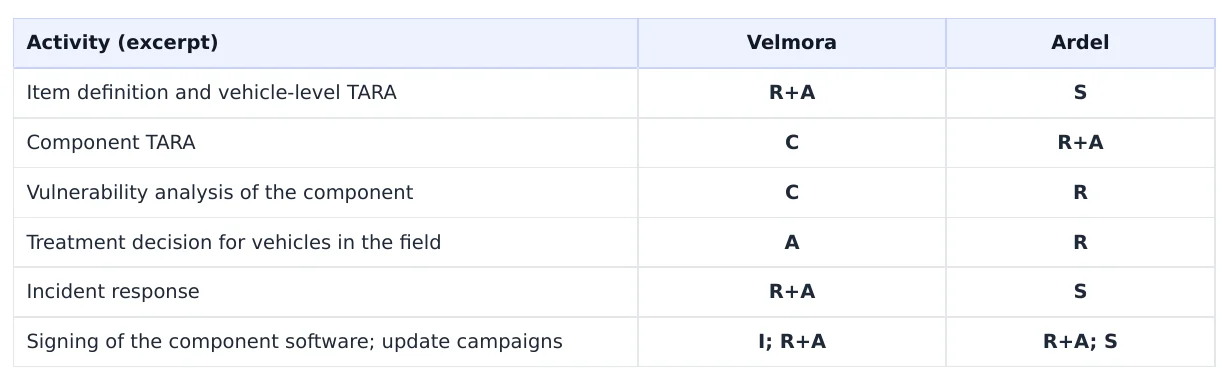
How does one threat connect to verification? 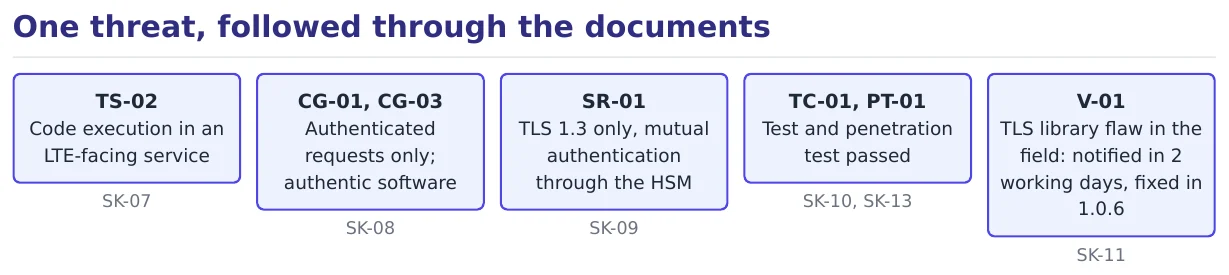
Filled modules
SK-01
Role and applicability
Define the supplier role and scope.
SK-02
Organisational cybersecurity evidence
Collect evidence of roles, processes and responsibilities.
SK-03
Supplier capability response
Answer customer questions about cybersecurity capabilities.
SK-04
Cybersecurity interface agreement
Agree who does what and which evidence is exchanged.
SK-05
Cybersecurity plan
Plan activities, owners and milestones.
SK-06
Component definition
Record boundaries, interfaces and assumptions.
SK-07
Component TARA
Analyse threat scenarios and decide how to treat risks.
SK-08
Goals, claims and concept
Translate risk decisions into cybersecurity goals, claims and a concept.
SK-09
Refined specification
Derive detailed requirements and retain traceability.
SK-10
Verification
Link requirements to verification activities and results.
SK-11
Vulnerability management
Record, assess and track vulnerabilities.
SK-12
Production, updates and end of support
Plan cybersecurity activities during production, updates and end of support.
SK-13
Cybersecurity case and release
Bring the cybersecurity argument and evidence together for the release decision.
SK-14
Gap assessment
Identify gaps and prioritise follow-up actions.
SK-15
Own products and CRA
Record a separate CRA applicability assessment for own products.